




Risk Management
- Related ESG :
- E S G
Management approach
Policy and approach
Toyobo Group, guided by its corporate philosophy of "Jun-Ri-Soku-Yu" (Adhering to reason leads to prosperity), aims to achieve sustainable growth and contribute to society by appropriately managing risks associated with its business activities. In our risk management activities, the risk-owning departments, such as front-line departments, identify and evaluate risks. These departments work in collaboration with corporate departments in charge of risk oversight to develop and implement risk mitigation measures. The Risk Management Department is responsible for planning and promoting these risk management activities.
The Group reviews significant risks that need to be addressed annually, and by conducting appropriate evaluation and management, strives to earn the trust of stakeholders such as customers, local communities, and shareholders.
< Basic policy on business risk >
1. Establish a mechanism to visualize and understand where risks lie and the scale of their potential impact across Toyobo Group.
2. Allocate resources appropriately to avoid or mitigate the identified risks.
3. Continuously improve and enhance risk management activities by applying the PDCA (Plan-Do-Check-Act) cycle.
4. Raise individual awareness and responsiveness to risks through information sharing and training, reducing knowledge gaps.
5. Foster a sense of ownership in risk management and promote team-based efforts to ensure participation by all members.
Business risks
The main risks recognized that could have a material impact on Toyobo Group's operating results and financial position are as listed below. The list does not include all the risks related to Toyobo Group.
Among the risks described below, statements regarding the future are based on the judgments of the TOYOBO Group as of the end of FY2026.
< Current and Highly Probable Risks >
- (1)
- Occurrence of disasters, accidents, and infections
- (2)
- Worsening of political and economic situations
- (3)
- Legal proceedings and other matters
< Medium- to long-term risks >
- (4)
- Purchase of raw materials
- (5)
- Product defects
- (6)
- Securing of human resources
- (7)
- Climate change
- (8)
- Environmental burden
- (9)
- Information security
- (10)
- Laws, regulations and compliance
- (11)
- Overseas business activities
< Financial risks >
- (12)
- Significant foreign exchange fluctuations
- (13)
- Significant increases in interest rates
- (14)
- Sharp declines in share prices
- (15)
- Impairment loss of fixed assets
Structure
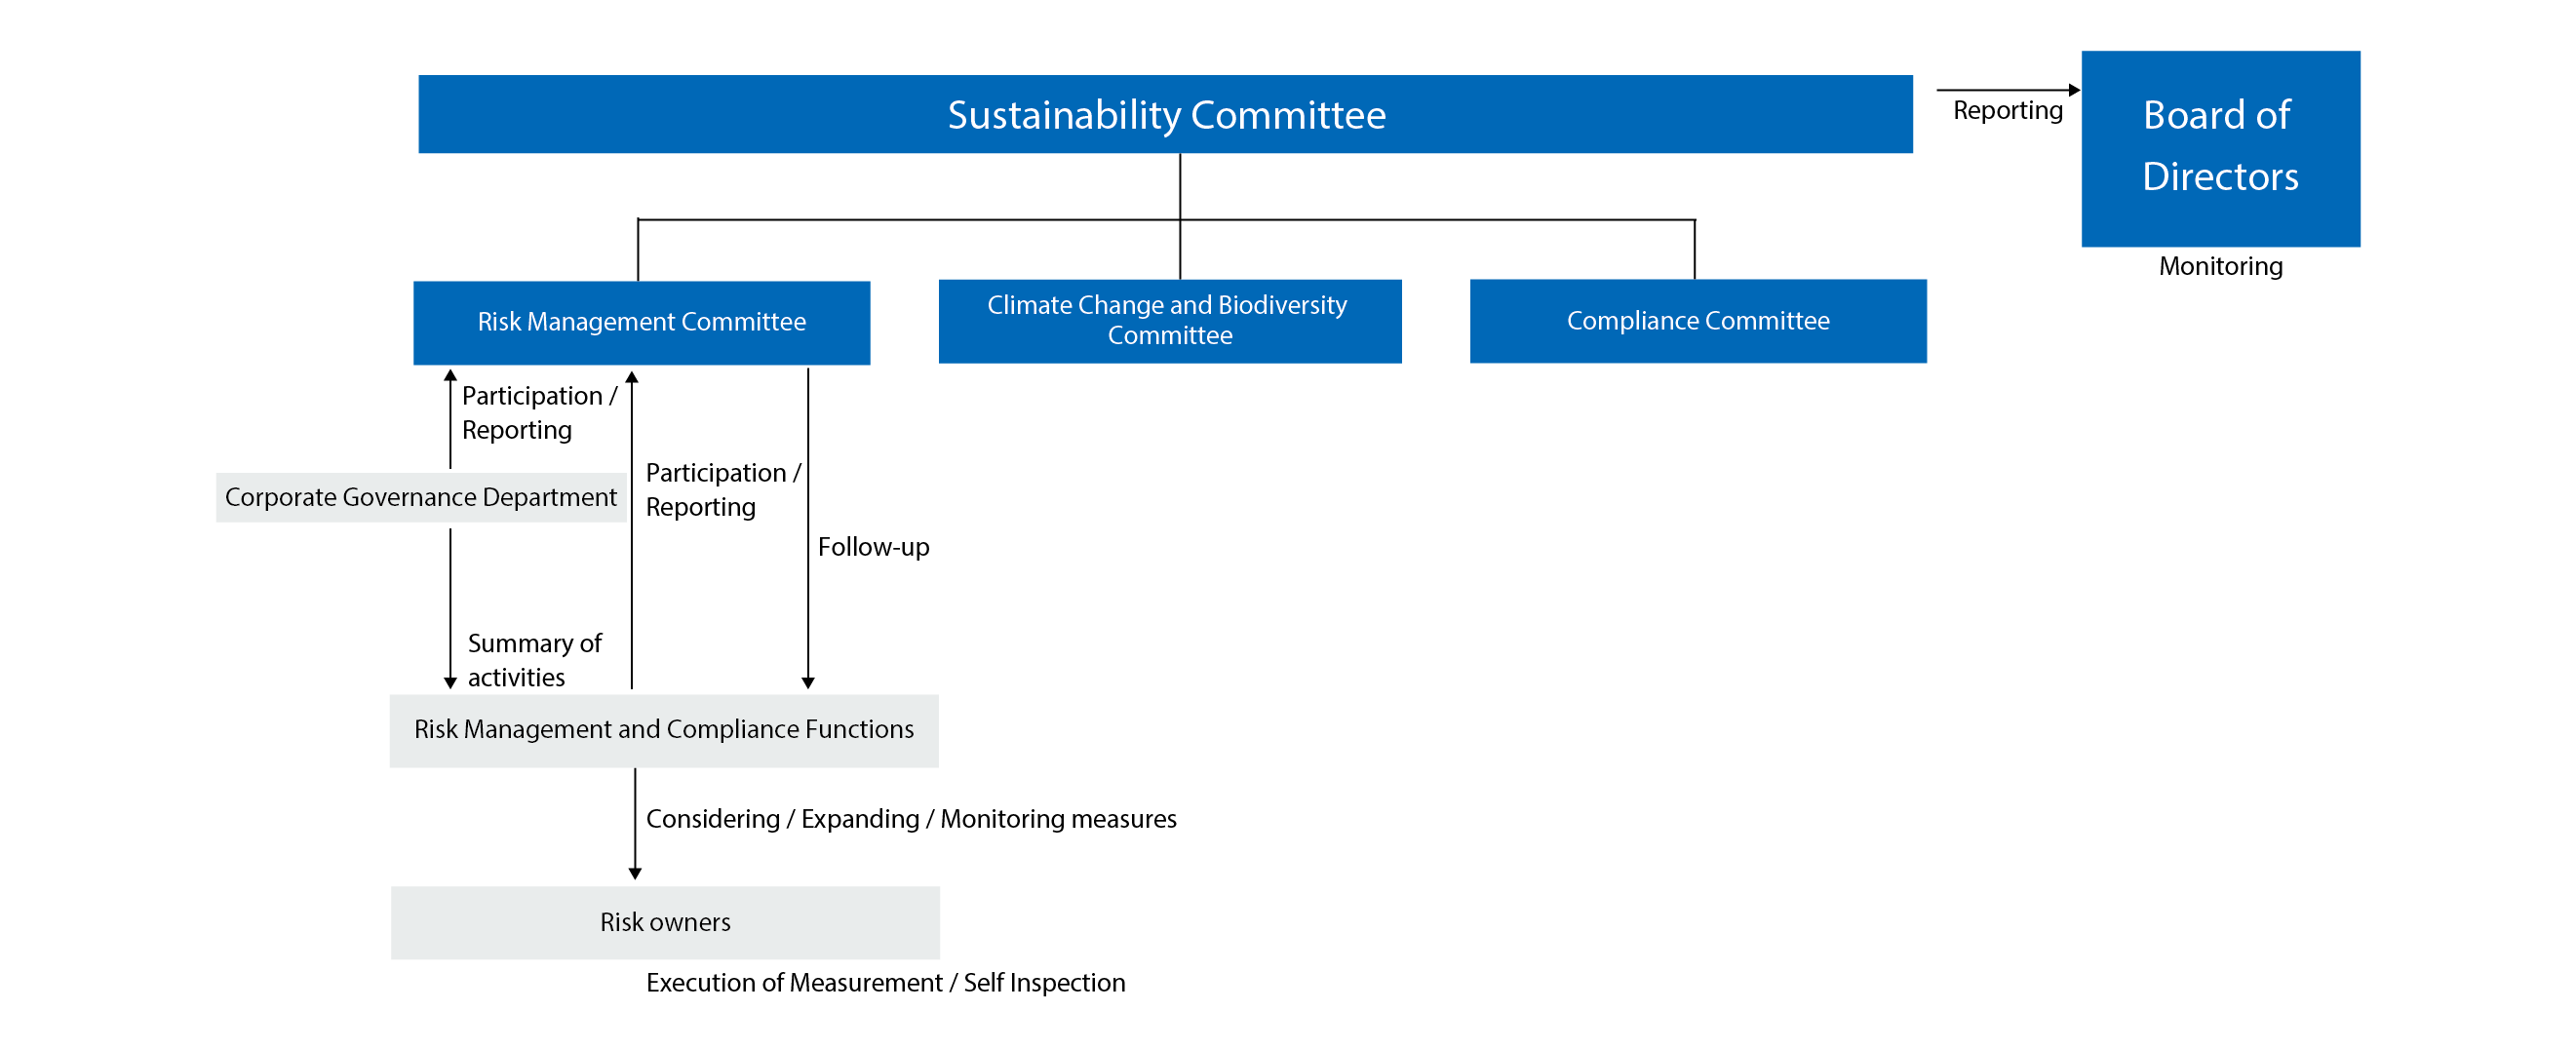
To clarify the role of the Risk Management Department as the department responsible for overseeing risks across the entire Group, the TOYOBO Group positioned it as an organization that will report directly to the President beginning in FY2027.
On April 1, 2021, Toyobo Group established the Risk Management Committee chaired by the President for centralized management of risks throughout the Group. The committee is attended by members of the Board of Management, including division heads and officers responsible for corporate staff divisions, and is held twice a year to promote Company-wide risk management activities.
The committee discusses and deliberates on significant risks that may impact the entire Toyobo Group, as well as major issues that require management decisions, with the aim of ensuring comprehensive understanding and strategic management and response. It formulates and monitors the direction and plans for specific risk management initiatives, verifies responses during emergencies, and examines countermeasures for emerging issues, thereby working to strengthen the overall risk management framework.
Management structures
Initiatives
As part of our management policy, we seek to be a company that is able to grow sustainably by shifting from the survival-based thinking of the past to a sustainable growth orientation. We establish self-directed management activities appropriate to business areas and roles, assess company-wide risks and work toward their prevention and early detection, and, united as a Group, will build a system to advance measures for preventing recurrence of risks.
As the starting point of these activities, the Company conducted an enterprise-wide risk assessment in 2021. Based on evaluations using two axes, impact and likelihood, significant risks were identified, and the departments responsible for each risk have been leading risk mitigation activities (ERM).
Since FY2023, risk assessments of significant risks have been conducted at all sites, including domestic and overseas Group companies. Through dialogue based on assumed risk scenarios, the Company assessed the status of risk responses at each site. As a result, it confirmed that there were no risks, including legal compliance risks, that would make it difficult for the Group to continue its business operations. At the same time, it began initiatives to address rapidly changing global conditions, including procurement instability arising from geopolitical risks and issues related to economic security.
For risk items that require measures based on common frameworks, such as cybersecurity response and virus infection prevention, we collaborated with departments responsible for risk management to implement uniform risk measures, regardless of domestic or overseas locations. However, for risk items requiring regulatory compliance measures, we have recognized that each Group company is taking independent risk measures in their operating regions.
Any detected items that are common across the Group and that require attention are reported to the Risk Management Committee. Group-wide risk reduction activities are undertaken in collaboration with the departments responsible for risk management, business divisions, and Group companies.
For high-risk items identified at each site through the risk assessment conducted in FY2026, the Company will evaluate the effectiveness of mitigation and management activities in FY2027 (BRM).
Information Security and Privacy
- Related ESG :
- S G
Policy and approach
Today, as the importance of information continues to grow, how a company utilizes necessary information, advances development of products and technologies, and develops businesses in line with the times is a crucial factor in the company's survival.
The improper management of information can also have severe repercussions for a company from legal and social standpoints. As stated in our TOYOBO Group Charter of Corporate Behavior, our Group must properly manage information and prevent problems involving information security from occurring if we are to contribute to society and remain a company that earns people's trust.
In other words, every officer and employee must recognize the importance of information security and the information assets that are the key to corporate survival, and, while effectively utilizing our information assets throughout the organization, maintains and secures the confidentiality, integrity, and availability of those information assets. Based on this thinking, our Group has declared our basic policies as follows:
< Information security policy (theme excerpts only) >
- 1. Management system
We will establish an information security management system with responsible executives placed at the top. and will strive for proper management in line with the importance of and risks to information. - 2. Legal compliance and internal regulations
We will establish internal rules in accordance with information security-related laws and ordinances, countries' national guidelines, and other social norms, and will take strict action against violators of these rules. - 3. Education and training
We will conduct education and training for our employees on an ongoing basis to ensure that information assets are used properly, and will work to enforce compliance with rules. - 4. Operation of information systems
We will enact appropriate measures and strive to ensure the stable operation of information systems stably to prevent unauthorized intrusion and the leak, falsification, loss, theft, destruction, obstruction of use, etc. of information assets. - 5. Handling of incidents
In the event of a problem involving information security, we will enact measures to minimize the damage, promptly investigate the cause, and strive to prevent recurrence.
Structure
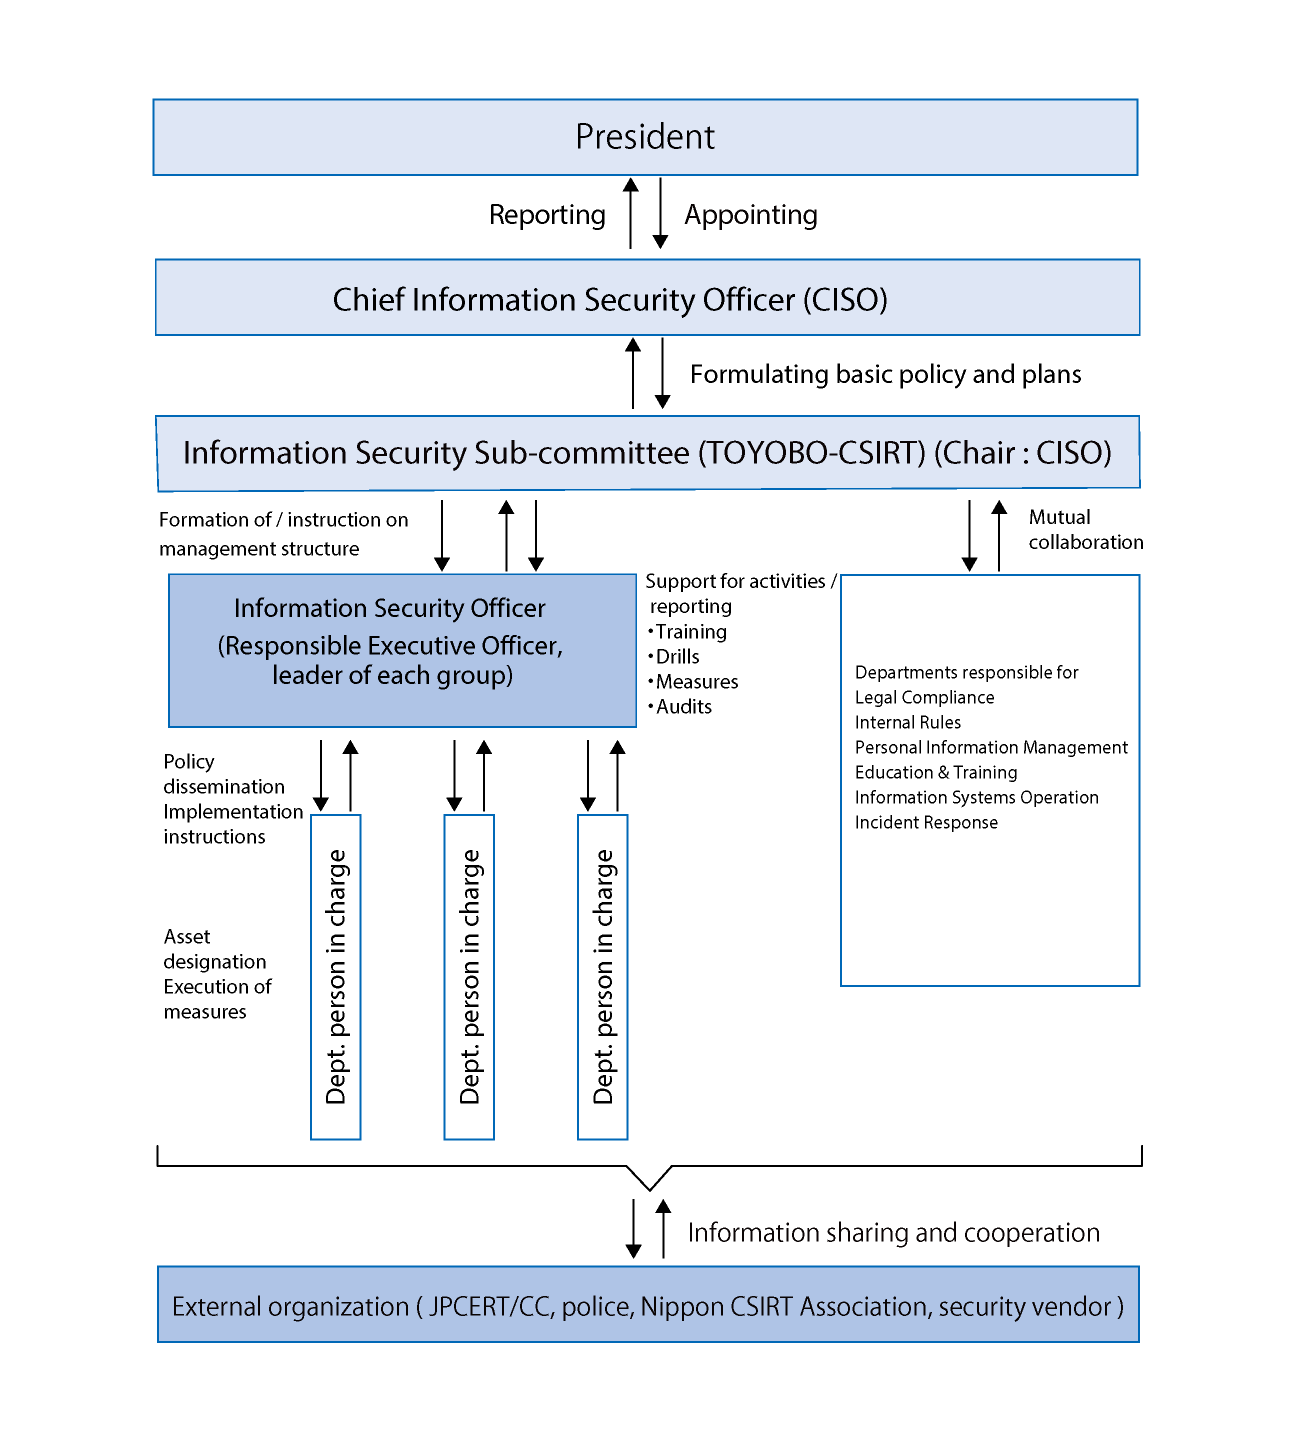
As an organization to promote information security initiatives, the TOYOBO Group has established the Information Security Sub-committee (TOYOBO-CSIRT*1), led by the Chief Information Security Officer (CISO) appointed by management. The sub-committee monitors the Company-wide status of information security, formulates basic policies, maintains management systems, and implements and supervises related measures.
To advance measures based on the decisions of TOYOBO-CSIRT, we have established a front-line operations team. We also convene TOYOBO-CSIRT on a regular basis to evaluate risk countermeasures, each time also reporting on activities related to information security.
By expanding the activities of TOYOBO-CSIRT throughout our entire Group, we will work to instill understanding of information security and enforce the protection of information assets, creating a state across the Group in which information security and privacy are properly protected and maintained.
Our Toyobo Transformation and Business Innovation Department, which has acquired ISO 27001*2 certification, undergoes a yearly external audit based on ISO 27001 to confirm proper operation of information security management. The Department conducts on-duty management at five business sites of the company (the head office, Research Center, Tsuruga Research and Production Center, Iwakuni Production Center, Inuyama Plant: 50% of all business sites), and also performs comprehensive management of other business sites through the Department's management system.
- Computer Security Incident
- An international standard for information security management systems
Toyobo Group information security management structure
We assign a person responsible for information security to each department and have built a company-wide information management system to ensure the required information security level.
Targets and indicators
< Targets >
Toyobo Group establishes a structure to ensure cybersecurity as well as deepening employee understanding of information security and thoroughly ensuring protection of information.
< Indicators and results >
| Initiatives | Indicators | Targets (FY2026) | Results (FY2026) |
|---|---|---|---|
|
|
|
|
|
|
|
|
|
|
|
- The scope covers TOYOBO CO., LTD., its subsidiaries, as well as affiliates accounted for by the equity method and over which Toyobo has significant influence.
Initiatives
Protection of personal information
Awareness of the protection of personal information is increasing worldwide. Toyobo Group has established internal regulations and ensures their dissemination to comply with personal data protection laws in various countries, including the Act on the Protection of Personal Information in Japan, the General Data Protection Regulation (GDPR) in the European Union, and the Personal Information Protection Law in China. These internal regulations are reviewed and updated as necessary.
We will continue to strengthen our systems for protection of the personal information of customers, our business partners, shareholders, and employees.
Promotion of digitalization
Digitalization is advancing rapidly with the development of IT. Amid this change, Toyobo Group is advancing the construction of an IT system infrastructure that encompasses the entire value chain and is tackling the transformation of our business style and the creation of new solutions, making full use of digital technologies. By doing so, we seek to not only improve the efficiency of work but also strengthen our provision of value to society and to customers.
Additionally, we have promoted the digitalization of business by actively incorporating IT in our operations, including streamlining sales activities through IT tools, using IT to enhance manufacturing control, and enhancing the efficiency of intellectual property management through AI.
The Digital Strategy Department established in FY2024 (currently the Toyobo Transformation and Business Innovation Department) was recognized for meeting the certification standards of the Ministry of Economy, Trade and Industry regarding the Group's DX initiatives and obtained DX Certification*1 in February 2024. After the two-year certification period, the Company was recertified on February 1, 2026. Additionally, in December 2024, the division won the IT Award*2 for the first time, in recognition of its organizational restructuring and efforts in IT talent development, aimed at expanding business through DX promotion.
The Transformation and Business Innovation Department serves as a bridge connecting digital and business. It has begun various initiatives to drive organizational and business transformation across the entire Company and its businesses. Going forward, the entire Company will collaborate even more closely to expand the scope and utilization of digitalization.
- This system is certified by the government under the Digital Governance Code compiled by METI. It recognizes companies that promote initiatives such as formulating visions and establishing systems for achieving DX, based on the Act on Facilitation of Information Processing.
- The IT Award is presented by the Japan Institute of Information Technology, a public interest incorporated association, to companies and organizations in Japan’s industrial sector that have made outstanding achievements in management innovation through the effective use of IT.
Education and awareness-raising activities
As a part of our education and awareness-raising activities, we deliver the “Cyber Security Communication” newsletter every month to all employees of Toyobo Group in Japan and overseas. We also conduct assessments of employees' understanding of information security twice a year to let employees self-check and reflect on their understanding of our education and awareness-raising activities.
Information security measures
Across the entire Group, including domestic and overseas affiliates, the Company promotes information security measures at the same level as those implemented at headquarters. Under a 24-hour security monitoring system utilizing AI, automatic blocking measures are taken when serious incidents are detected to minimize damage. The Company also continuously conducts incident response training to strengthen response capabilities. In addition, mechanisms are in place to ensure the smooth escalation of major incidents to the risk management framework. Furthermore, taking supply chain risks into account, the Company is strengthening its IT-BCP*1 initiatives and enhancing business continuity systems for emergencies.
To ensure the security of customer information and internal information containing confidential data, the Company continuously monitors emerging threats and implements appropriate measures for both IT and OT*2, including enhanced monitoring, vulnerability remediation, and intrusion prevention. In addition, to promote and accelerate business innovation through DX and enable the utilization of data both within Group companies and with external parties, the Company is developing IT infrastructure that provides secure access regardless of user location.
- A plan to restore critical systems promptly and support business continuity in the event of disasters or system failures.
- IT (Information Technology) and OT (Operational Technology).
Protection of information in outsourcing
When outsourcing information assets containing confidential information, the Company has established outsourcing management rules for the following procedures: (1) evaluation and contracting of outsourcing partners; (2) monitoring of operations after the contract has been concluded; and (3) handling of information assets after the contract has been terminated.
When newly implementing operations to be outsourced (hereinafter referred to as “specified operations”), the department outsourcing the specified operations evaluates whether or not the candidate companies conform to outsourcer evaluation criteria in accordance with these rules. After the selection, the department submits the outsourcer evaluation results to the head of the information security department for approval. In addition, it is also stipulated that the implementation status of specified operations is to be regularly evaluated by the head of the information security department.
Outsourcer evaluation criteria are clearly stated in the Information Security Policy.
Initiative participation
Under the idea that we must address cyber attacks not only in our Group companies and supply chains but across society as a whole, we engage in active information sharing in cooperation with the JPCERT Coordination Center and the Nippon CSIRT Association.
Business continuity management (BCM)
Policy and approach
Business Continuity Management (BCM) within our Group is based on our corporate philosophy of "Jun-Ri-Soku-Yu" (Adhering to reason leads to prosperity). It is designed to support the Group’s sustainable growth by recognizing potential threats to our organization and their impact and responding effectively when disruptions occur. In practicing BCM, we prioritize the protection of human life, work to prevent secondary damage, and aim for a swift recovery to fulfill our social responsibilities and support the business continuity of our customers and partners through effective response measures.
Business continuity plan (BCP)
Policy and approach
Toyobo Group prioritizes the safety of employees and their families above all else and is committed to balancing the fulfillment of our supply responsibilities as a manufacturer with harmonious coexistence with the local environment and society. By detecting emergencies at an early stage and responding swiftly with necessary actions, we work collectively across the organization to minimize damage and achieve rapid recovery.
Structure
Under the Risk Management Committee, we have established a BCM Subcommittee composed of members selected from each department to promote BCM across the Group. This subcommittee leads the formulation of Business Continuity Plans (BCPs), training, and drills within each department. It also serves as the contact point for gathering and disseminating information and coordinating necessary actions to ensure business continuity in the event of major emergencies such as large-scale earthquakes. When an emergency occurs or is anticipated, a Company-wide BCP Task Force is established to quickly bring the situation under control through prompt and effective action.
Initiatives
In FY2025, we formulated the TOYOBO Group Business Continuity Plan (BCP) Guidelines to address the potential impact of a major earthquake (seismic intensity of upper 5 or higher), with a focus on a possible Nankai Trough Earthquake. These guidelines define procedures for assessing damage, communication systems, the designation of command personnel, recovery structures and roles, and task prioritization. We are also working to identify and manage risks across the entire supply chain. The Company also recognizes increasingly sophisticated cyberattacks associated with advances in digital technologies as a significant management risk and has therefore established a BCP that assumes the occurrence of cyberattacks. In FY2026, based on BCPs developed by each business unit, training exercises simulating major earthquakes were conducted at key sites, and lessons learned from these exercises have been incorporated into normal operations. In addition, the Company strives to identify and manage risks throughout the supply chain arising from geopolitical risks that are increasingly important from an economic security perspective. In procurement, it promotes sourcing from multiple countries and regions, while in logistics it works with logistics providers to establish alternative transportation methods and routes. Going forward, the Company will continue to conduct regular employee education and training to enhance awareness of business continuity and strengthen resilience.